



Brushing Scams: The Merchant’s Guide to Fake Orders
“Brushing” is the practice of shipping cheap or empty packages to real addresses so the sender can post verified-purchase reviews under those names.
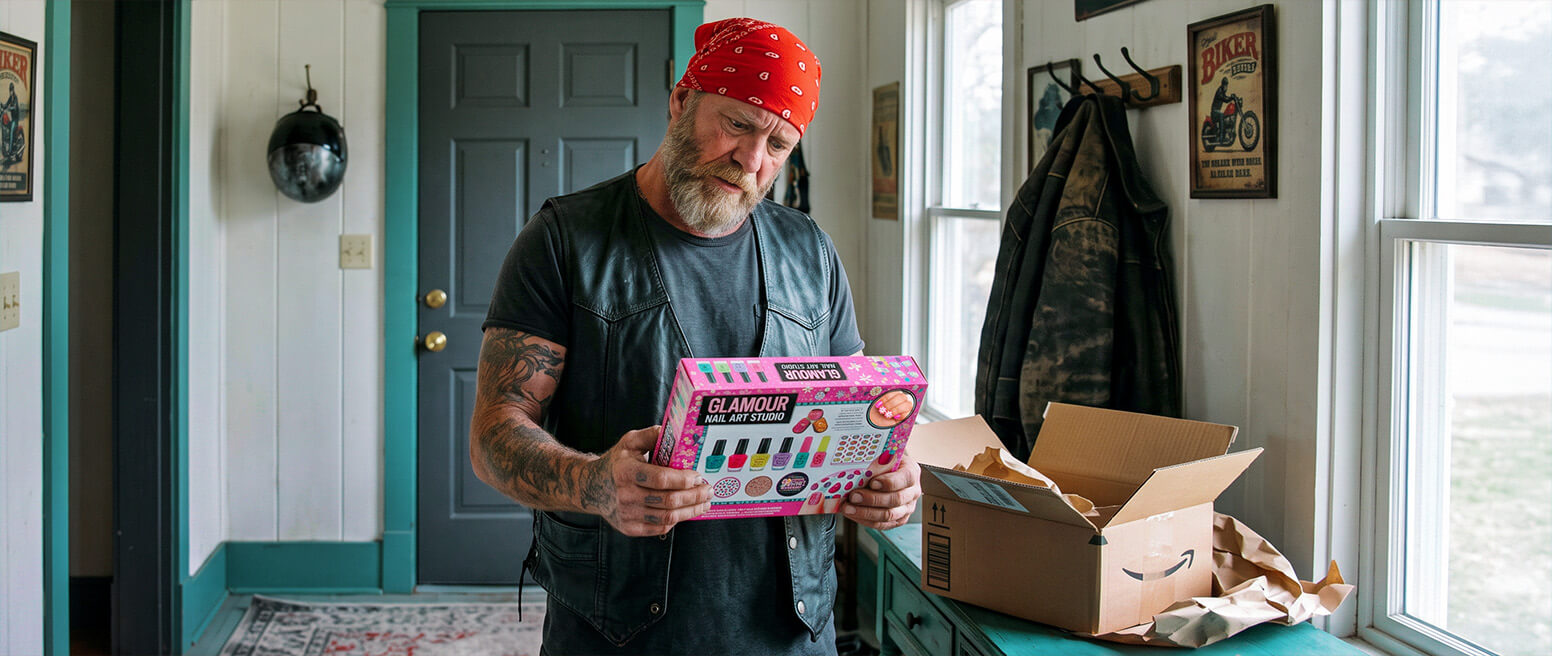
I did a cursory search to see what would come up, and I found that most of the results were fixated on the box. What’s inside it? Why did it show up? Is it dangerous to open? Can you keep it?
Those may all be pertinent questions from a consumer standpoint. For a merchant, though, the box is beside the point.
What matters is that somewhere upstream of that delivery, a real order was placed through a real storefront, and it was paid for with a real payment instrument. After all, platforms don’t hand out verified-purchase badges for orders that were never completed or never paid.
So an order went through someone’s checkout. It might have been yours. And, as I’ll explain, that could cause problems for you.
Recommended reading
- Package Redirection Scams: Tips to Stop Them From Happening
- Cookie Stuffing: Still a Threat in 2026. Here’s How it Works
- How to Identify & Prevent Shipping Scams in 2026
- How to Prevent Second-Party Fraud: Tools That Work
- Fight Second-Party Fraud Chargebacks: Here’s What Works
- Second-Party Fraud Liability: Who Pays for the Loss?
What is Brushing?
- Brushing
Brushing is a form of review and ranking manipulation. A seller or their agent ships low-value or empty packages to real addresses, then uses those recipients’ names to place orders and post reviews that platforms treat as verified purchases.
[noun]/brəsh • ing/
Marketplaces generally won’t treat an order as “valid” until something ships. So, brushers ship the cheapest thing that will generate a tracking number. A seed packet. A silicone ring. An empty box.
The contents were never the point. Recipients puzzle over why someone would send them a random phone case, and the answer is that nobody chose the phone case for them. It was selected for weighing almost nothing and costing almost nothing, because its only job was to produce a tracking number.
- Seed packet
- Silicone ring
- Empty box
- The sender, as a marketing cost
- A brushing service, with prepaid cards
- Stolen or stored card credentials
Brushing is not the same as:
- Triangulation fraud: This moves real goods to a real buyer who paid somewhere else. Brushing has no real buyer at all.
- Card testing: This exists to validate stolen credentials. Brushing may piggyback on it, but the goal is a review, not a working card.
- Paid review fraud: Here, a scammer buys reviews outright. Brushing manufactures an actual purchase, so the review qualifies as verified.
What Does the Sender Get Out of a Brushing Attack?
The main goal is to artificially inflate the seller’s conversion and customer satisfaction rating, thereby exposing their products to more buyers.
Verified-purchase reviews carry substantially more weight with shoppers — and with the algorithm — than unverified ones. Sales volume feeds search placement. Conversion sends signals that can influence listing position directly.
The practice originated on Chinese marketplaces, where it became widespread enough that Alibaba flagged it in its IPO prospectus. China’s eCommerce laws now prohibit the practice outright. That history matters mainly as context for where brushing operations tend to be based and why they often target Western marketplaces from a distance.
How Can Merchants End Up Involved in a Brushing Scheme?
Brushing can be attributed to one of three sources: your vendor could be engaging in brushing on your behalf, your store may be used as a pass-through for brushing attacks, or you could be targeted by a malicious competitor.
You could be involved in a brushing scheme, completely unbeknownst to you, through one of three entirely unrelated avenues:
Consequences for Those Caught Engaging in Brushing
The FTC prohibits creating, selling, or procuring fake reviews, and can impose penalties that cost tens of thousands of dollars per fake review.
Like I mentioned earlier, the FTC Consumer Review Rule bans brushing schemes. It also lays out consequences for those who get caught engaging in the practice.
Penalties run up to $53,088 per violation, as of 2025. The figure adjusts annually for inflation, though, so the number I quoted should be treated as a ballpark figure that is meant only to give you a frame of reference for your potential exposure.
The FTC began using the rule as an enforcement tool in late 2025. Suspected violators will see a formal warning letter, demanding corrective action on a short deadline.
The FTC fines are not the only potential risk, though. On the platform side, consequences may include review removal, listing suppression, withheld funds, and permanent loss of selling privileges.
Fraud-coded chargebacks count toward your chargeback ratio regardless of where they came from. The accounting does not make allowances for the fact that the orders were somebody else’s scheme running through your store.
How to Tell If Someone is Running a Brushing Scheme Through Your Store
There are multiple red flags that suggest someone may be involved in a brushing attack, observable at the order level, the review level, or the customer portfolio level.
Brushing can be hard to diagnose. But, there are signals that you may be able to pick up on at the order level, as well as in customer reviews, and in aggregate transaction data.
Order-Level Signals
- Repeat shipping addresses appearing across unrelated customer names.
- Orders clustered at the lowest value that still qualifies for whatever the brusher needs.
- Accounts created shortly before their first and only purchase.
- Recurring combinations of address and payment instrument.
- Orders that fulfill cleanly and produce no post-purchase contact of any kind.
Review-Level Signals
- Verified reviews posting faster than your delivery timelines could support.
- Review text that doesn’t describe the product, or describes a different one.
- Clusters of reviews from accounts with almost no history.
- Review volume that outpaces your actual order volume.
Portfolio-Level Signals
- Address convergence across accounts with no apparent relationship.
- Conversion rates on specific listings that don’t match the traffic those listings receive.
- Promotional or new-customer offers redeemed at volumes your real growth doesn’t explain.
There is a caveat here. Nearly every red flag I outlined above could also be present with an ordinary purchase.
Gift orders go to addresses that aren’t the buyer’s. Household accounts produce address and device variance. New customers are, definitionally, new.
A rule that declines orders on any single one of these will inevitably cost you more in false declines than all combined brushing activity was going to cost you in the first place. You need to score the signals, require several to converge on the same order, and scale your scrutiny to what’s actually at risk.
-
Order A
A first-time customer
1 of 5 signals
- Address shared by unrelated names
- Account created just before the order
- Lowest qualifying order value
- Address and payment pair seen before
- No contact after purchase
-
Order B
A gift from a new customer
2 of 5 signals
- Address shared by unrelated names
- Account created just before the order
- Lowest qualifying order value
- Address and payment pair seen before
- No contact after purchase
-
Order C
Several signals on one order
5 of 5 signals
- Address shared by unrelated names
- Account created just before the order
- Lowest qualifying order value
- Address and payment pair seen before
- No contact after purchase
Each of these signals also turns up on ordinary orders. It’s the convergence on one order that points to brushing.
What to Do if Your Store is Being Targeted
Before you respond to anyone, determine which of the three positions you’re in. Is your vendor engaging in brushing on your behalf? Is your store being used as a pass-through for brushing attacks? Or, are you being targeted by a malicious competitor?
-
PerpetratorYour vendor is doing itWhat you seeReviews, velocity and placement delivered by a launch consultant or reputation manager.The riskPlatforms and the FTC hold you responsible, even if you didn’t know. Up to $53,088 per violation (2025).What to doTerminate the vendor and document it, with the root cause, corrective action and preventive controls.
-
InfrastructureYour store is the vehicleWhat you seeModest orders that fulfill normally and generate zero customer contact, until the disputes arrive.The riskFraud-coded chargebacks count toward your ratio, whoever’s scheme it was.What to doScore the order-level signals and build the evidence file from your order and fulfillment records.
-
VictimYou’re the targetWhat you seeOrders to undeliverable addresses, automatic refunds, a rising return rate and negative reviews.The riskEnforcement reads the pattern as yours. Sellers report multi-day closures, with appeals refused.What to doReport through the platform’s own channels and keep dated records of every report.
Pull your order records, your review timelines, and every contract you have with a marketing vendor. Then, build the evidence file. Compile dated vendor agreements and the scope of work you actually bought. Order and fulfillment records covering the disputed window. Copies of any reports you filed about suspicious activity. Correspondence with the vendor.
By examining all of these pieces of evidence in connection to one another, you stand a reasonable chance of piecing together what happened.

If a Vendor is Responsible
Your response needs a root cause, the corrective action you’ve already completed, and the preventive controls you’ve put in place with named owners. Terminate the relationship and document that you did.

If You Were Targeted
Report through the platform’s own channels and keep dated records of every report. This matters more than it sounds. Contemporaneous reports are what separates a seller who was attacked from a seller who noticed a pattern and said nothing, and is therefore viewed as complicit. That distinction often decides the outcome.
Brushing is one of the few eCommerce fraud problems where the merchant can be perpetrator, infrastructure, or victim, depending on circumstances they may not control. If disputes are already arriving and you’re not sure which category you’re in, our team can help you read the pattern.
FAQs
What is a brushing scam?
Brushing is when a seller or their agent ships cheap or empty packages to real addresses, then uses those names to place orders and post reviews the platform counts as verified purchases. The goods are incidental. The purpose is to generate verified reviews and sales volume that improve a listing’s ranking.
Why would a seller ship a package nobody ordered?
Because most marketplaces won’t validate an order until something ships. A delivery scan is what turns a fake order into a verified purchase, so the brusher sends the cheapest item that will produce one. The recipient’s address is needed to complete the order, not because anyone wanted them to have the product.
Who pays for brushing packages?
Often the sender absorbs it as a marketing cost. Sometimes a brushing service uses prepaid or disposable payment methods. In some cases orders are funded with stolen or stored card credentials, and that’s when chargebacks start reaching the merchant who processed them.
Can brushing get my seller account suspended?
Yes. Brushing constitutes both review manipulation and ranking manipulation under most marketplace policies, and platforms generally hold sellers responsible for the actions of vendors acting on their behalf, including where the seller was unaware. Consequences range from review removal and listing suppression to withheld funds and permanent loss of selling privileges.
Is brushing illegal?
In the United States, the FTC’s Consumer Review Rule prohibits creating, selling, or procuring fake reviews, with liability where a business knew or should have known. Civil penalties reach $53,088 per violation as of 2025, a figure that adjusts annually, so check the FTC for the current amount. Brushing is also prohibited under China’s eCommerce laws, where the practice originated.
What should I tell a customer who got a package they didn’t order?
Tell them they can keep it, that their address was more likely harvested than their account compromised, and that they shouldn’t scan any QR code included in the package. Encourage them to report it to the marketplace. Resist the urge to recommend a credit freeze by default, since a brushing operation typically needs a deliverable address rather than access to anyone’s accounts.