



BIN Attack Fraud: How the Scam Works & How to Prevent It
A merchant who absorbs several thousand tiny declines in an afternoon will usually assume, reasonably enough, that someone has stolen a batch of card numbers and is busy spending them. The more interesting answer, and the one I think merchants consistently underrate, is that nothing was stolen at all.
The numbers were generated, but most of them belong to nobody. The checkout is the instrument being used to work out which ones actually work. Nothing was taken; something was guessed.
In this post, we’ll look at how a BIN attack works, what one attack can cost the merchant caught in the middle of it, how to spot one in your own transaction data, and what the card networks can now do about it.
Recommended reading
- Package Redirection Scams: Tips to Stop Them From Happening
- Cookie Stuffing: Still a Threat in 2026. Here’s How it Works
- How to Identify & Prevent Shipping Scams in 2026
- Brushing Scams: The Merchant’s 2026 Guide to Fake Orders
- How to Prevent Second-Party Fraud: Tools That Work
- Fight Second-Party Fraud Chargebacks: Here’s What Works
What is a BIN Attack?
- BIN Attack
A BIN attack occurs where a scammer sets a BIN (or “Banking Identification Number”) in place, then cycles through numbers programmatically, trying to guess a valid combination of a 16-digit credit card number, expiration date, and CVV number.
[noun]/bin • uh • tak/
Take any payment card and look at the long number on the front. The opening digits are the Bank Identification Number, which identifies the institution that issued the card. BINs are not confidential; they are published to the merchants, processors, and service providers that need them to route a transaction.
Learn more about BIN codesWhat sits after the BIN is an account number and a single check digit, calculated from everything before it based on the Luhn formula. That last digit is the reason a BIN attack is not the random guessing it gets described as.
The software does not assemble numbers at random because a number assembled at random fails the check before it ever reaches an issuer. It produces, at volume, candidates that could be valid card numbers.
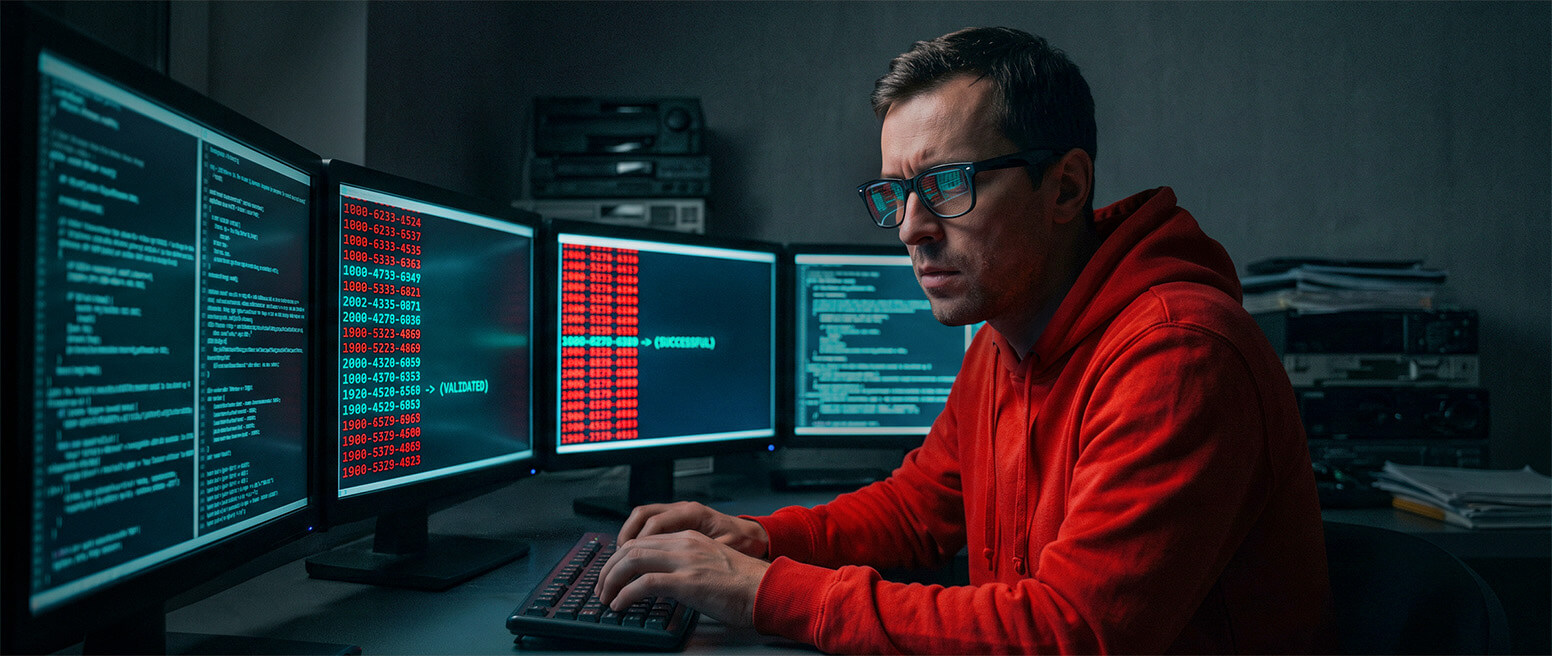
The perpetrator then take the list of potential card numbers and engages in high-volume card testing, typically using automation to submit multiple transaction attempts per second. A generated number becomes a working number at the moment an authorisation comes back approved. It is primitive. But with bot infrastructure behind it, primitive is sufficient. A single operation can put thousands of candidates through in seconds, across dozens of merchants at once, and needs only a small fraction of them to come back approved.
Nothing is stolen.The rest is guessed.
01 Published
Unknown
Six digits name the issuing bank.
02 Generated
- 41472048 11 ··
- 41472002 77 ··
- 41472091 34 ··
- 41472060 18 ··
- 41472027 85 ··
Thousands More
Software fills the rest. Almost all fake.
03 Tested
- 48 11Declined
- 02 77Declined
- 91 34Declined
- 60 18Approved
- 27 85Declined
One by One
The rare approval is a real card.
The checkout does the sorting.
Mastercard’s guidance to merchants treats card testing, carding, enumeration, and account testing as four synonyms for the same behaviour.
How Does a BIN Attack Work?
So, how do scammers actually go about conducting a BIN attack? Here’s a general overview of the steps in the process:
- A scammer selects the BIN code for their targeted bank. These numbers are accessible to the public, making them relatively easy to obtain.
- Using card-generator software, the scammer produces thousands of candidate numbers on the targeted bank’s BIN, each one built to satisfy the Luhn check so it survives basic validation before anyone looks at it.
- The next step involves validating these credentials. The scam artist finds a suitable online retailer or donation page for this purpose.
- Card testing commences. The fraudster, typically employing bots to automate the process, makes repeated small purchase attempts using each newly generated card number.
- The fraudster keeps a record of any card details which generated a successful transaction. These valid numbers can be exploited for additional fraudulent transactions.
Bear in mind that the CVV is verified separately from the authorisation decision itself. The issuer returns a result for the check alongside its answer, and unless a merchant has set a rule to decline on a mismatch, a transaction can be approved even with the wrong CVV attached to it.
This will naturally result in a surge of unusual activity for the merchant. Many merchants impose velocity limits to block sudden surges of suspicious activity for this reason. To combat this, scammers might involve multiple online retailers and services as part of a single BIN attack.
BINs were set at six digits for most of the industry’s history. Since April 2022, when Visa began assigning only eight-digit BINs under the revised ISO/IEC 7812-1 standard, it has been six or eight, depending on when the range was allocated. Both six- and eight-digit BINs remain in circulation alongside one another.
How BIN Attacks Affect Banks, Merchants, & Customers
BIN attack scams have detrimental effects on everyone involved in a transaction. Some of the impacts each can expect include:
The Enumeration Ratio Was Written for This
According to Visa, enumeration is “the criminal practice of submitting fraudulent card-not-present transactions into the payments ecosystem in order to obtain valid payment information.” BIN attacks are thus a form of enumeration. This is relevant because, since April 2025, Visa has tracked enumeration incidents as a category in their own right under the Visa Acquirer Monitoring Program.
The program fact sheet sets two conditions, and both have to be met before a merchant is identified. First the VAMP Enumeration Ratio, defined as enumerated authorisation transactions divided by total authorisation transactions, must reach 20% of total transactions. The VAMP Enumeration Transaction Count, including both approved and declined enumeration attempts, must also reach 300,000 in the month. Visa determines which transactions were enumerated through its Account Attack Intelligence scoring, which means the figure a merchant is measured against is Visa’s rather than its own.
VAMP is exclusive to the Visa ecosystem. But, Mastercard operates a comparable scheme under its Transaction Processing Excellence program, assessed based on repeated authorisation attempts against the same account at the same acceptor, with thresholds that vary by region.
Defeat new fraud tactics and protect your revenue from scammers.
Request a Demo
It’s true that these programs are administered at the acquirer level. It’s also the case that card schemes tend to move the cost of an ecosystem problem onto the participant best placed to instrument it. In card-not-present commerce, that participant is almost always the merchant.
The reporting that produces the number belongs to Visa and reaches merchants through their acquirers. It is not something a business can derive from its own decline logs. So, it is necessary for merchants to gauge their relative risk on an ongoing basis. Realistically, the 300,000 floor puts most merchants outside the program altogether, which makes knowing where a business sits relative to that floor the only sensible first move
How to Detect a BIN Attack
Generally speaking, detecting a BIN attack involves identifying unusual patterns of credit card transactions. While it may not always be possible to prevent a BIN attack, timely detection can go a long way to mitigate potential damage.
The authorisation log is the first place to look. A spike in declines sharing one prefix is not a processing fault. It is reconnaissance, and the approvals inside it are the cards that will be used somewhere else, days later, against a merchant who never saw the testing. So, if you identify a batch of suspicious transactions with shared BINs and similar card numbers, that is a clear giveaway.
Other tactics you may use to spot a BIN attack include:
- Unusually Small Transactions: Look for numerous small transactions, especially from the same source. This suggests card testing.
- High Number of Declined Transactions: A sudden surge in the number of declined transactions could indicate a BIN attack, as fraudsters often have to try many numbers before finding a valid card.
- Repeated Transactions from the Same IP Address: Multiple attempts from the same IP address, particularly if many of them are declined.
- Rapid Succession of Transactions: A high number of transactions are attempted in rapid succession.
- Geographic Inconsistencies: Transactions are coming from an IP address in one country, but the cards being used are issued in another.
- Multiple Cards from the Same BIN: Seeing multiple transaction attempts, all using different cards but having the same BIN and with similar products.
- Unusual Time of Transactions: Transactions are attempted at odd hours when normal card usage is low.
- Suspicious Merchant Account Behavior: Multiple transaction attempts followed by an unusually high chargeback ratio on a particular merchant account.
- Abnormal Transaction Volumes: A sudden surge in the number of transactions or total transaction value.
- Incomplete Cardholder Information: Transactions are being attempted with incomplete or incorrect cardholder information. This includes the CVV number, the expiration date, or the address details.
If any of these signs are detected, the appropriate parties should be alerted immediately to help prevent further fraudulent activity.
10 Ways Merchants Can Prevent BIN Attacks
Now that we have a good idea of what to look for and how to spot a potential attack, let’s talk about how we can use this information to help prevent a BIN attack from happening in the first place.
Fortunately, you have a wide expanse of tactics and tools at your disposal which may help counteract BIN attacks. The ten practices I’ve outlined below should provide a firm starting point:
No system is 100% foolproof. However, by being proactive and implementing multiple security measures, businesses can significantly reduce their risk of falling victim to BIN attacks and card testing fraud.
What Your Customers Can & Cannot Do
Unfortunately, there isn’t much that can be done to keep a bot from guessing a cardholder’s credit card number. So long as these tools exist, they will be used by fraudsters for nefarious purposes. Plus, there is almost no way for consumers to know when they’ve been targeted until it’s too late.
That rules out a whole category of response. Customer education does not reduce enumeration traffic, and a business treating cardholder vigilance as part of its defense has left the work undone.
Now that said, there are two things which do carry over. Wallet payments like Apple Pay and Google Pay hide the actual card number from the retailer, which takes it out of circulation before anyone can guess at it. And a cardholder who catches a small, unauthorised charge early and reports it is often the first signal anyone gets that a shop has been used as a testing ground.
Multifaceted Strategies Work Best
Preventing BIN attacks and card testing fraud is only part of the battle. A multifaceted fraud prevention strategy is the only genuinely effective approach, because it is the one that lets a merchant detect criminal activity like a BIN attack and first-party threats like friendly fraud in the same pass, while streamlining the payment process rather than obstructing it. The two threats arrive from opposite directions and the defense against them is singular. That is the whole argument.
Looking to improve your fraud prevention efforts and limit your exposure to other sources of loss? Chargebacks911® can help. By combining advanced fraud detection with comprehensive chargeback management, we enable you to get back to focusing on what matters most: growing your business and serving your customers. Contact us today for a no-obligation analysis.
FAQs
What is a brute force BIN attack?
“Brute force” describes the method rather than a separate kind of attack. Software takes a known Bank Identification Number, generates large volumes of candidate card numbers on it, and submits them until some are approved. The numbers are not stolen from anywhere. They are manufactured, then tested until the working ones identify themselves.
What is the solution to BIN attacks?
From a merchant’s standpoint: velocity limits to block card testing, bot detection at the checkout, and a decline threshold that cuts off repeated attempts. None of it stops the numbers being generated somewhere else. It stops a merchant’s own checkout from being the place where the guessing gets confirmed.
What does BIN mean on a credit card?
BIN stands for Bank Identification Number, the opening digits of a card number that identify the issuing institution. It was six digits for most of the industry’s history, and has been six or eight since Visa began assigning eight-digit ranges in April 2022. Both lengths are still in circulation. More on BIN codes here.
What is the difference between card testing and BIN attack?
They describe one activity from two angles. A BIN attack is the whole operation, starting from a known BIN and working toward valid card details. Card testing is the step at which the transaction in question is validated, and where small transactions are pushed through merchant checkouts to find out which numbers come back approved.
How do you read a BIN on a card?
A BIN number is typically represented by the first six numbers on a cardholder’s credit or debit card.